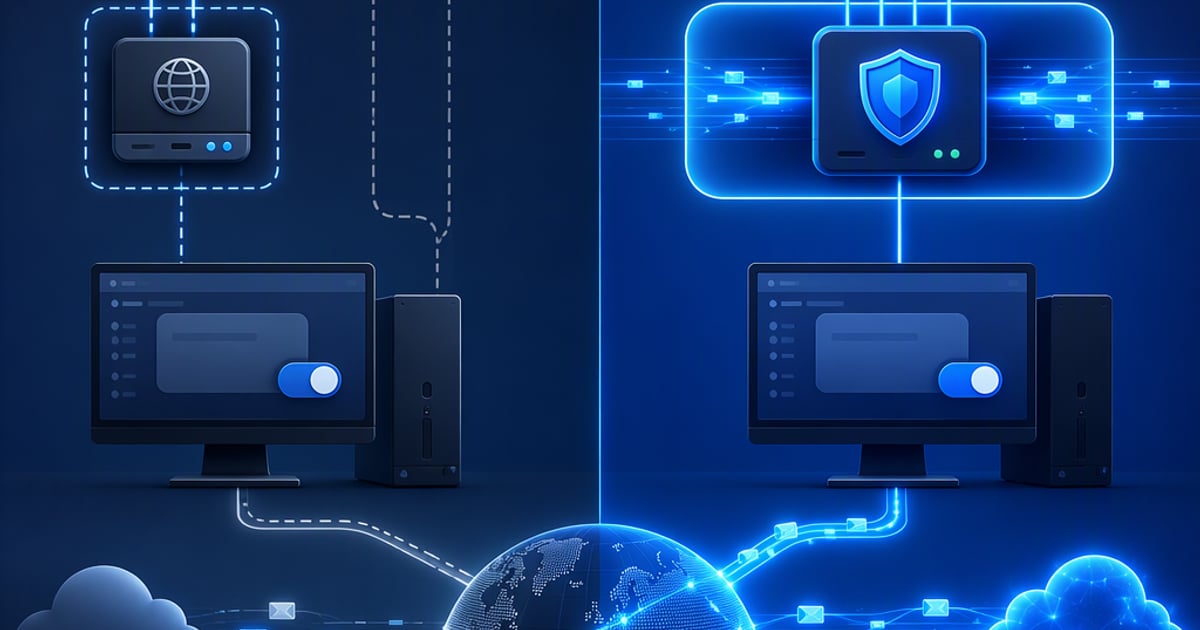
A system proxy is a setting that applications may read and follow, so it only covers software that cooperates. TUN mode creates a virtual network interface and redirects routing to it, so it captures IP packets from almost every program, cooperative or not. As of November 2026, that one distinction explains most "the browser works but the terminal does not" complaints.
What does a system proxy actually capture?
A system proxy is a proxy address (host and port) stored in the operating system's network settings. It captures only the traffic of programs that look the setting up and choose to honor it. Nothing forces an application to comply, so coverage depends entirely on each program's own networking code.
Chromium-based browsers such as Chrome and Edge read the OS setting by default, as do many desktop apps built on the platform's standard networking libraries. Plenty of software ignores it. Firefox has its own proxy preferences, command-line tools usually read environment variables such as http_proxy, https_proxy and all_proxy instead, and programs with a hand-rolled network stack (some games, updaters and runtimes) may not consult anything at all.
- Application layer: the program hands the proxy a hostname and asks it to connect on its behalf.
- Usually no administrator rights: it is a simple setting that is easy to switch on and off.
- Mostly TCP: an HTTP proxy relays HTTP requests and HTTPS tunnels (via
CONNECT). UDP-based traffic such as QUIC, voice chat and many games cannot ride an HTTP proxy. - Tool by tool: the shell, git, Docker and package managers each have their own proxy settings.
What does TUN mode capture instead?
TUN mode creates a virtual network interface and points the routing table at it, so the operating system hands raw IP packets to the VPN client before they leave the machine. Because the capture happens below the application, it covers TCP, UDP and DNS queries from programs that know nothing about proxies.
A TUN device is a feature of the OS kernel. The Linux kernel documents it as the universal TUN/TAP driver, Windows clients commonly build on the Wintun driver, and macOS exposes utun interfaces. The client reads packets from this interface, wraps them in its tunnel or proxy protocol, and sends them to the server through your real network adapter. Replies travel the opposite way. Creating the interface and editing routes needs elevated privileges, which is why TUN mode asks for administrator or root permission, or installs a helper service, the first time you turn it on.
How do the two modes differ side by side?
The practical difference is coverage and cost: a system proxy is light and limited to cooperating apps, while TUN mode is broad but touches the whole network stack. The table summarizes what changes for the traffic you care about.
| Aspect | System proxy | TUN mode |
|---|---|---|
| Where it works | Application layer (proxy requests) | Network layer (IP packets) |
| Apps that ignore proxy settings | Not covered | Covered |
| UDP and QUIC | Not through an HTTP proxy | Covered when the client's protocol carries UDP |
| DNS | Depends on the app: some resolve locally, some send the hostname to the proxy | The client can capture DNS queries at system level |
| Privileges | Usually none | Administrator or root for the interface and routes |
| Typical failure | An app silently connects directly | Bad routes or a conflicting VPN break connectivity |
How can I check what is really being captured?
Check three things in order: the system proxy setting, the environment variables in the shell you are using, and the routing table. Together they tell you which mechanism, if any, applies to a given program.
# macOS: show the system proxy settings
scutil --proxy

# Linux and macOS: proxy-related environment variables in this shell
env | grep -i proxy

# Linux: addresses and routes (look for the virtual interface)
ip -br addr
ip route show

# Windows: WinHTTP proxy and the routing table
netsh winhttp show proxy
route print

# Any OS: see whether curl picked up a proxy from the environment
curl -v https://example.com -o /dev/null
With curl -v, a line starting with "Uses proxy env variable" means curl took a proxy from your environment. With TUN mode on, the routing table should show routes that point at the new virtual interface. Some clients add a lower-metric default route, others add two half-default routes (0.0.0.0/1 and 128.0.0.0/1); the exact approach varies by client. Note that on Windows, netsh winhttp shows the WinHTTP setting, which is separate from the per-user proxy page in Settings.
What goes wrong with TUN mode, and how do I fix it?
Most TUN problems come from routing conflicts, not from the mode itself. Two programs fighting over the default route, a stale route left after a crash, or a missing permission account for the majority of cases.
- Two VPNs at once: run only one TUN-based client at a time; they compete for the same routes.
- Permission denied: if you dismissed the administrator prompt, the interface is never created, so restart the client and approve it.
- LAN devices unreachable: printers and NAS boxes on
192.168.x.xaddresses need to be excluded from the tunnel; check the client's bypass or local-network option. - Some sites hang while small pages load: encapsulation adds overhead, and a packet size (MTU) that is too large is a classic cause. If your client exposes an MTU setting, lowering it is the usual fix.
- Wrong DNS answers: confirm whether the client captures DNS and which resolver it uses.
Which mode should I use?
Use a system proxy when you only need one browser covered, and TUN mode when you need terminals, desktop apps or games covered without configuring each one. You can enable both, but troubleshooting is easier with one at a time.
- Browsing only in a Chromium-based browser: the system proxy is the simpler option.
- Command-line tools, desktop apps and anything you cannot configure: use TUN mode.
- UDP-heavy apps such as voice chat or games: TUN mode, if the client's protocol carries UDP.
- Headless servers: set proxy environment variables or per-tool settings instead, since TUN needs an interface you may not want to add.
Where AnboVPN fits
AnboVPN's official clients support both TUN mode and application-level smart routing, so you can capture the whole device or decide per application what goes through the VPN. One account can be used on any number of devices, billed by data plan, and new accounts receive a one-time 1 GB of data valid for one month. You can get the clients for Windows, macOS, iOS, Android and Linux from the AnboVPN download page.